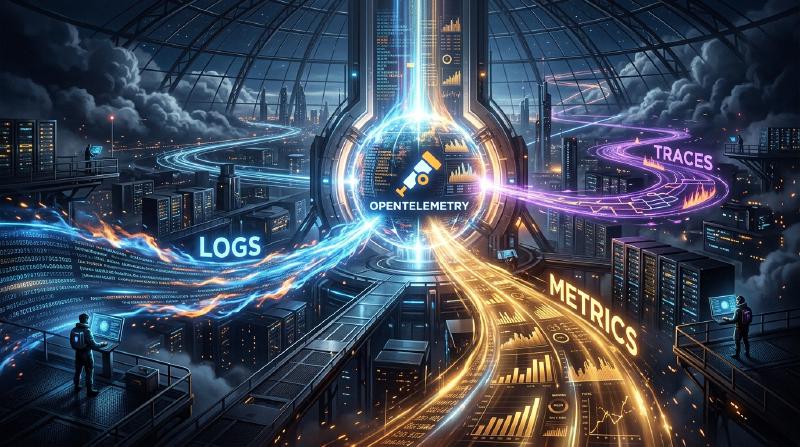
An operational guide to a vendor-agnostic standard observability platform.
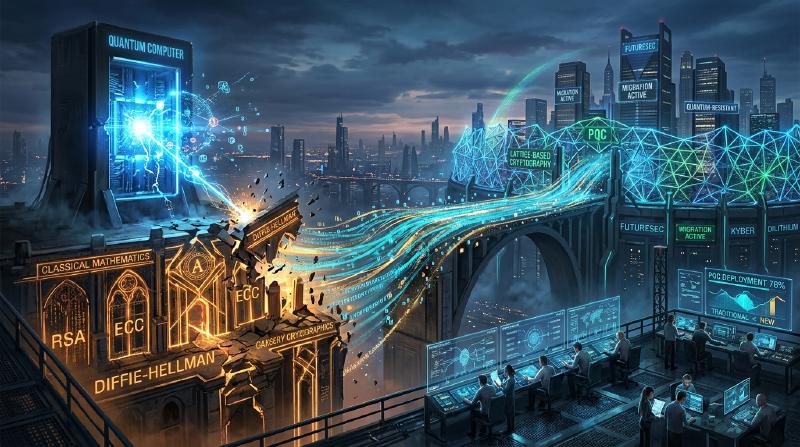
An enterprise migration guide and crypto-agility following NIST standardization
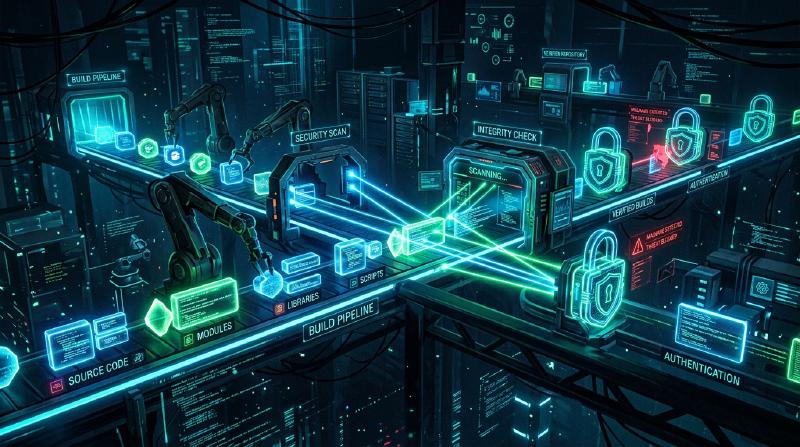
A complete guide to supply chain defense in GitHub Actions and CI/CD. From the lessons of the SolarWinds incident, we thoroughly explain the generation and management of SBOM (SPDX/CycloneDX), the 4 levels of SLSA, and how to implement signature verification using Sigstore.
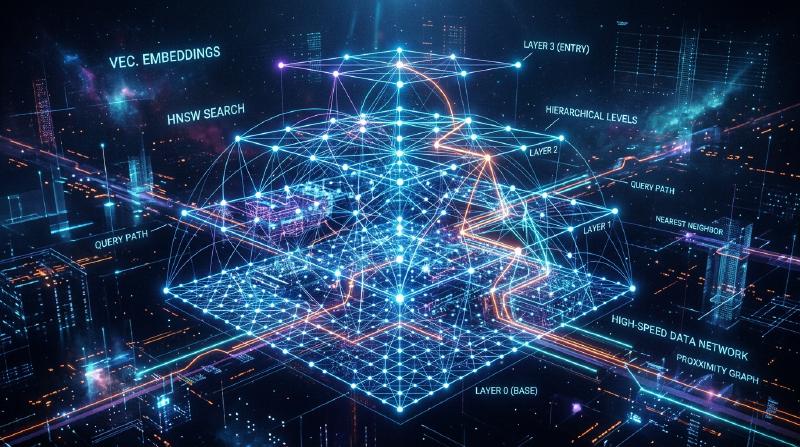
An in-depth explanation of the high-speed search technology underpinning RAG.
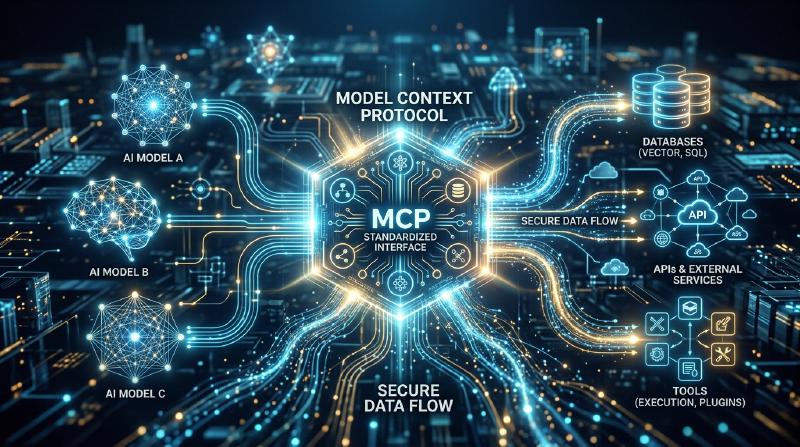
Standardization of APIs, agents, and security.
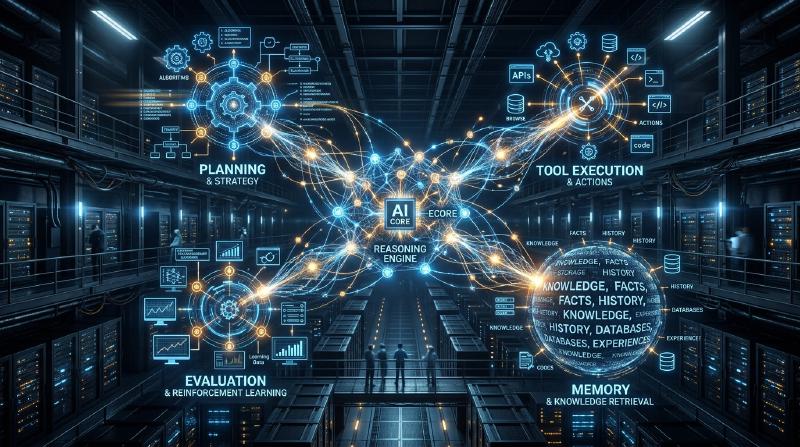
A comprehensive guide to building next-generation AI systems, covering AI agent evolution, ReAct patterns, Plan-and-Solve, memory mechanisms, reflection, and multi-agent systems.
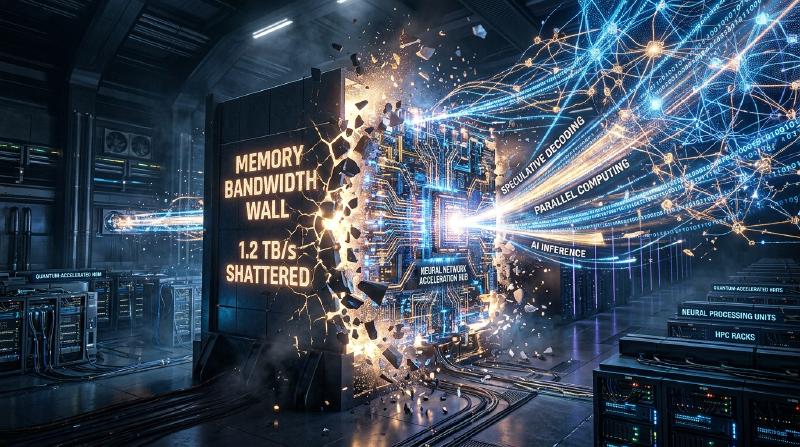
A deep dive into llama.cpp and quantization. From the memory bandwidth wall to PagedAttention and Speculative Decoding, we thoroughly explain the bottlenecks of Transformer inference and the latest optimization technologies.
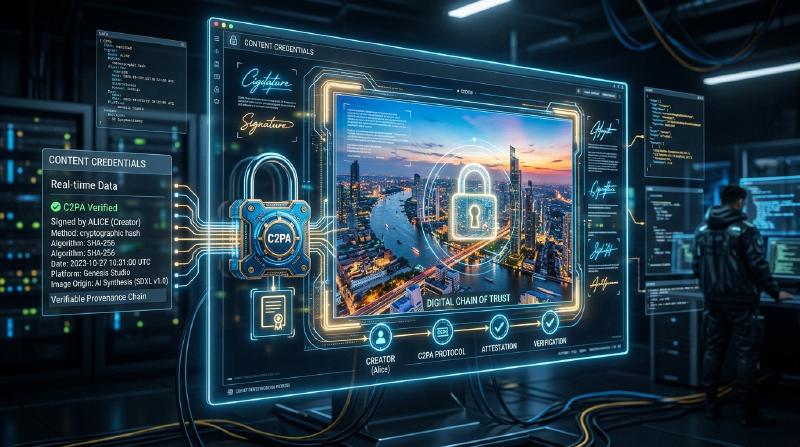
Anti-deepfake measures. Explaining the verification of provenance tampering rather than determining content authenticity.
How conflicts are automatically resolved with Google Docs-style synchronization.
An in-depth explanation of the public key cryptography behind passkeys, the FIDO/WebAuthn specifications, and why they are phishing-resistant.
Practical examples of running not only graphics rendering, but also image processing and machine learning (touching upon W3C specification updates).
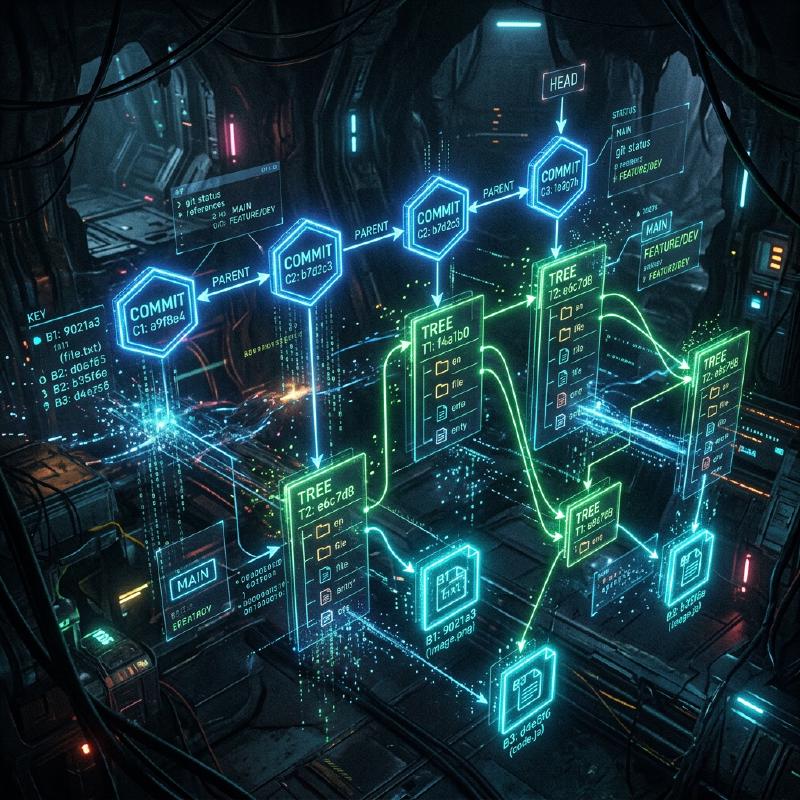
Delving deeply into Git's philosophy and operations from the perspective of its data structures.
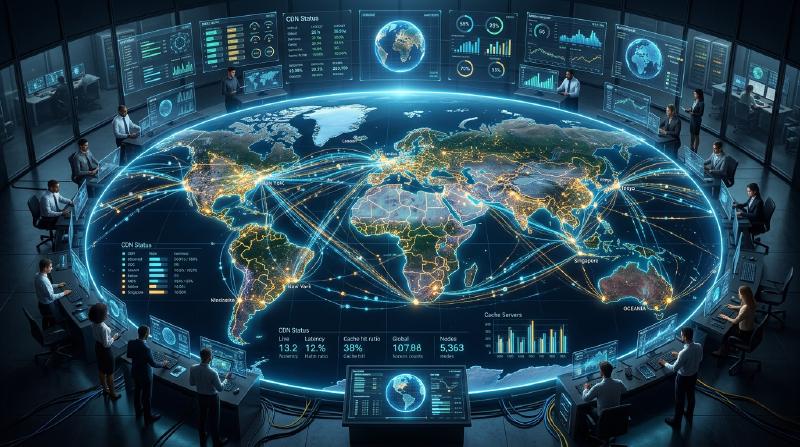
An in-depth explanation of the core technologies behind Content Delivery Networks (CDNs), including caching, edge servers, and Anycast routing. Discover the secrets to making the internet faster and more stable.
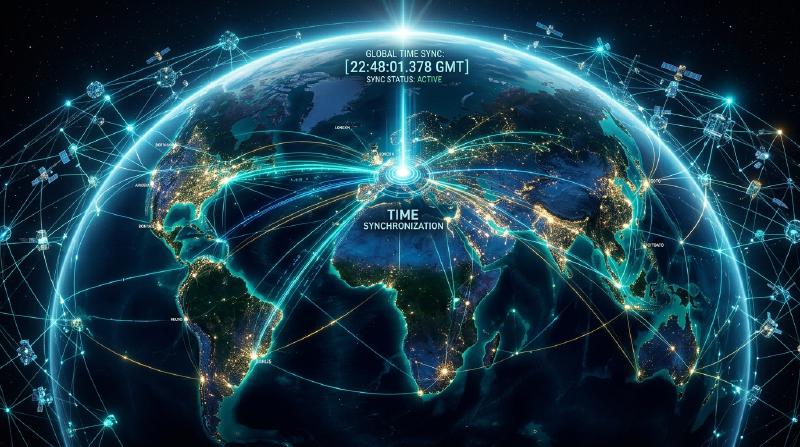
A detailed explanation of the mechanism of 'NTP', the time synchronization technology connecting the latest research on optical lattice clocks and the modern IT infrastructure it supports.
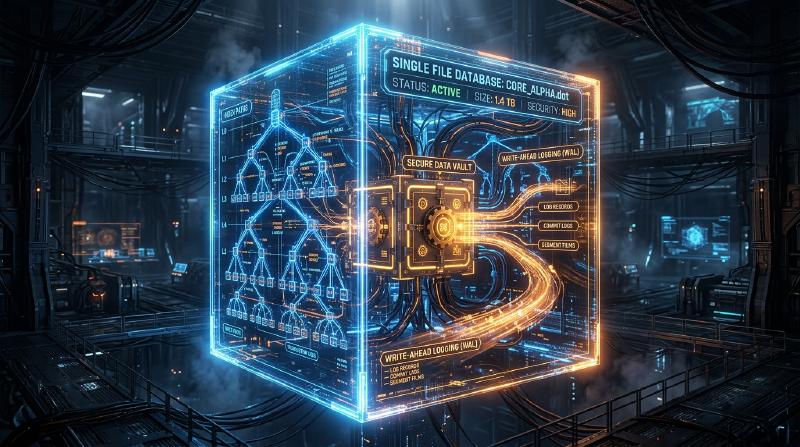
A practical guide explaining how SQLite implements B-trees, WAL, and locks in a single file to achieve secure transactions.
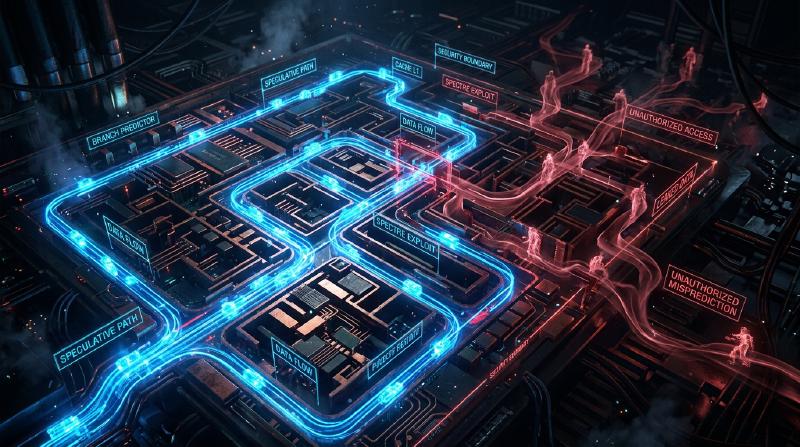
An explanation of 'speculative execution', the mechanism that dramatically sped up modern CPUs, and the background of how it created the historic security vulnerability 'Spectre', discussing the trade-off between performance and security.
A massive routing technology that serves as the foundation for TCP/IP and DNS.
Behind the scenes of email delivery and spam filtering.
A detailed explanation of how NAND flash memory, the primary storage media of SSDs, works, why its lifespan decreases with rewriting, and lifespan extension technologies such as wear leveling and TRIM.
Complementing semiconductor corporate history from a technical perspective. Explaining the amazing mechanism of EUV lithography and why ASML monopolizes it.